Cybersecurity in IoT: Protecting U.S. Infrastructure with 4 New Protocols in 2026
Cybersecurity in IoT: Protecting U.S. Infrastructure with 4 New Protocols in 2026
The dawn of the Internet of Things (IoT) has brought unprecedented connectivity and efficiency to virtually every sector of our lives. From smart homes to intelligent transportation systems, IoT devices are transforming how we interact with our environment and manage critical operations. However, this pervasive integration comes with a significant caveat: cybersecurity. The U.S. national infrastructure, encompassing everything from power grids and water treatment facilities to transportation networks and defense systems, is increasingly reliant on IoT technologies. This reliance, while beneficial, simultaneously exposes these vital systems to a burgeoning landscape of cyber threats. Therefore, bolstering IoT cybersecurity protocols is not merely an option but an imperative for national security and resilience.
As we look towards 2026, the urgency to fortify these digital bulwarks has spurred the development and anticipated implementation of several groundbreaking protocols. These new standards aim to address the unique vulnerabilities inherent in IoT ecosystems, which often involve a vast number of diverse, resource-constrained devices, complex supply chains, and distributed architectures. This article will delve into the critical importance of these advancements, highlighting four pivotal new IoT cybersecurity protocols poised to redefine the protection of U.S. infrastructure.
The Escalating Threat Landscape: Why New IoT Cybersecurity Protocols are Crucial
The current state of IoT security is often characterized by fragmentation, legacy systems, and a lack of standardized practices. This creates fertile ground for cyber adversaries, ranging from state-sponsored actors to sophisticated criminal organizations, to exploit vulnerabilities. Attacks on critical infrastructure can have catastrophic consequences, leading to widespread service disruptions, economic damage, and even loss of life. Consider the potential impact of a coordinated cyberattack on a national power grid, or the disruption of a major port’s automated logistics system. The stakes could not be higher.
The sheer volume of IoT devices, projected to reach tens of billions globally by 2026, significantly expands the attack surface. Each device, if not properly secured, can serve as an entry point for malicious actors. Furthermore, many IoT devices are designed for specific functions with minimal computational power, making it challenging to implement traditional, resource-intensive security measures. Supply chain vulnerabilities, where malicious code or hardware can be injected during manufacturing or distribution, also pose a substantial risk that current security paradigms struggle to fully address.
In response to these growing challenges, governmental bodies, industry consortia, and academic institutions are collaborating to develop and deploy more robust and adaptive IoT cybersecurity protocols. These efforts are not just about patching existing holes; they are about building a more resilient and secure digital foundation for the nation’s critical assets. The focus is on proactive defense, threat intelligence sharing, and the implementation of security features that are intrinsic to the design of IoT systems, rather than bolted on as an afterthought.
Protocol 1: Enhanced Device Identity and Attestation (EDIA)
One of the foundational challenges in IoT security is verifying the legitimacy and integrity of devices connected to a network. Traditional authentication methods often fall short in dynamic IoT environments where devices may frequently join and leave networks, and where their physical security cannot always be guaranteed. Enhanced Device Identity and Attestation (EDIA) emerges as a critical new protocol aiming to address this fundamental issue.
What is EDIA?
EDIA goes beyond simple credential-based authentication. It establishes a cryptographically verifiable, immutable identity for each IoT device from its manufacturing stage throughout its lifecycle. This identity is tied to a secure hardware root of trust, making it highly resistant to tampering and spoofing. Furthermore, EDIA incorporates continuous attestation mechanisms, allowing network systems to regularly verify the integrity of a device’s software, firmware, and configuration in real-time. If any unauthorized modification or compromise is detected, the device can be automatically isolated or quarantined, preventing it from becoming a pivot point for an attack.
How EDIA Fortifies U.S. Infrastructure
- Supply Chain Security: By embedding verifiable identities at the point of manufacture, EDIA helps to mitigate risks associated with untrusted hardware or software components introduced during the supply chain. This ensures that only genuine and uncompromised devices are integrated into critical infrastructure.
- Prevents Device Impersonation: Malicious actors often attempt to impersonate legitimate devices to gain unauthorized access or inject false data. EDIA’s strong cryptographic identities make such impersonation exceedingly difficult, ensuring that only authenticated devices can communicate within the network.
- Real-time Integrity Monitoring: The continuous attestation feature provides an ongoing security posture assessment. This means that even if a device is compromised after deployment, the system can quickly detect the anomaly and take corrective action, significantly reducing the window of opportunity for attackers.
- Automated Response: EDIA facilitates automated responses to security incidents. When a device fails attestation, predefined policies can trigger automatic isolation, alerting, and forensic data collection, minimizing manual intervention and reaction time.
The implementation of EDIA will be a significant step towards creating a ‘zero-trust’ environment for IoT devices within critical infrastructure, where every device’s identity and integrity are continuously verified, rather than implicitly trusted.
Protocol 2: Quantum-Resistant Cryptography for IoT (QRCI)
The advent of quantum computing, while still in its nascent stages, poses a significant long-term threat to current cryptographic standards. Many of the encryption algorithms widely used today, particularly public-key cryptography, could theoretically be broken by sufficiently powerful quantum computers. Given the long operational lifecycles of many critical infrastructure IoT devices, anticipating and preparing for this future threat is paramount. Quantum-Resistant Cryptography for IoT (QRCI) is being developed precisely for this purpose.
Understanding QRCI
QRCI involves the adoption of new cryptographic algorithms that are believed to be secure against attacks from both classical and quantum computers. These ‘post-quantum’ algorithms are based on different mathematical problems than current standards, making them resilient to quantum computational power. For IoT, this means developing lightweight, efficient quantum-resistant algorithms that can be implemented on resource-constrained devices without compromising performance or battery life.
QRCI’s Impact on U.S. Infrastructure Security
- Future-Proofing Data Security: QRCI ensures that sensitive data transmitted and stored by IoT devices in critical infrastructure remains confidential and integral for decades to come, even as quantum computing capabilities advance. This is vital for long-term data archives and communications.
- Protecting Long-Lived Assets: Many infrastructure components, such as smart grid sensors or industrial control systems, have operational lifespans of 20-30 years or more. Integrating QRCI now prevents these devices from becoming vulnerable to quantum attacks in the future, avoiding costly and disruptive retrofits.
- Securing Command and Control: The integrity and confidentiality of command and control signals for critical infrastructure (e.g., opening/closing valves, adjusting power flows) are paramount. QRCI will ensure these communications cannot be eavesdropped upon or tampered with by quantum-enabled adversaries.
- Enhanced Authentication and Key Exchange: QRCI will provide quantum-resistant methods for device authentication and secure key exchange, further strengthening the overall security posture and complementing protocols like EDIA.
The transition to QRCI will be a complex undertaking, requiring careful planning and standardization. However, its proactive adoption is essential to maintain the confidentiality and integrity of U.S. infrastructure data against emerging threats.
Protocol 3: Adaptive Threat Intelligence and Response (ATIR)
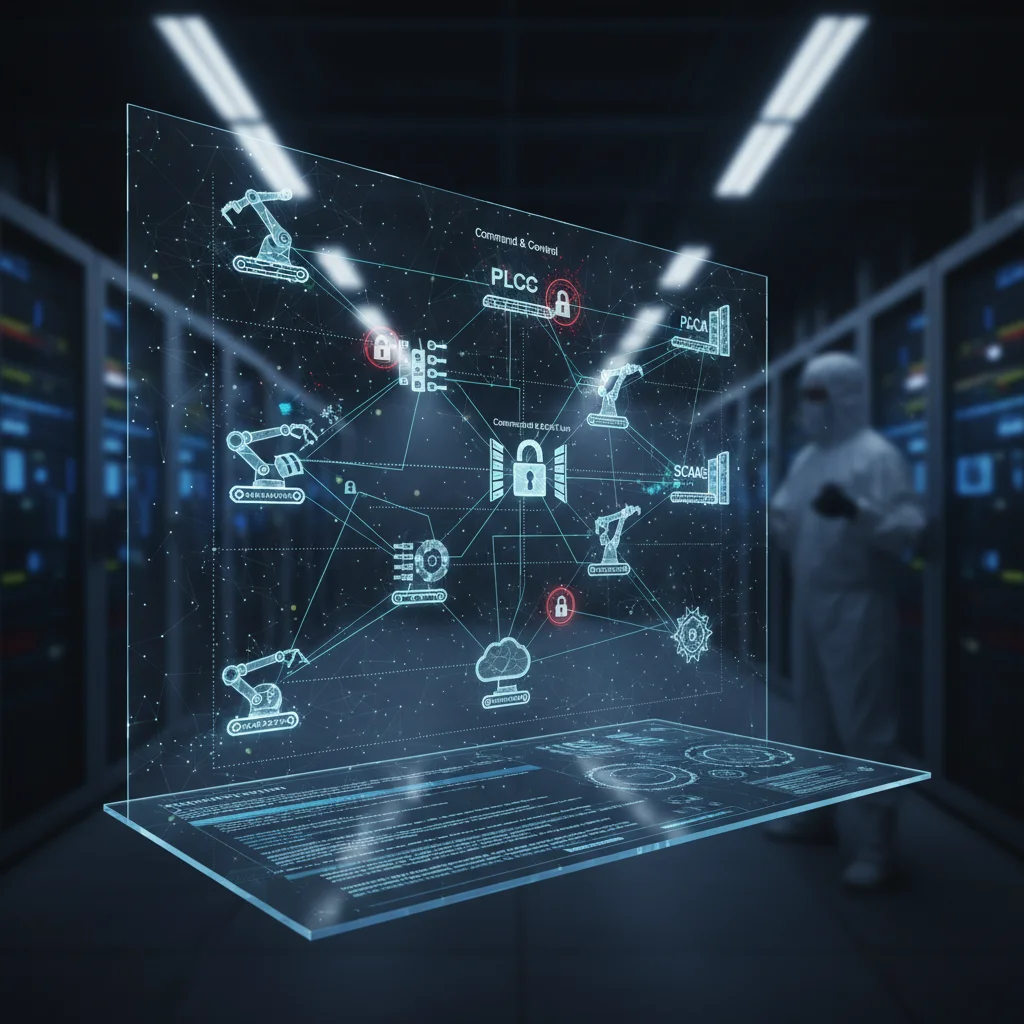
The nature of cyber threats is constantly evolving, with new attack vectors and malware emerging daily. Traditional, static security measures are often insufficient to keep pace with this dynamic landscape. Adaptive Threat Intelligence and Response (ATIR) is a new paradigm designed to bring real-time, context-aware security to IoT deployments within U.S. critical infrastructure, making IoT cybersecurity protocols more dynamic.
Defining ATIR
ATIR leverages artificial intelligence (AI) and machine learning (ML) to collect, analyze, and disseminate threat intelligence across interconnected IoT systems. It moves beyond signature-based detection to identify anomalous behaviors, zero-day exploits, and sophisticated persistent threats. Key components of ATIR include:
- Centralized Threat Intelligence Platforms: Aggregating data from various sources, including global threat feeds, internal network telemetry, and device-specific logs.
- Behavioral Analytics: ML models establish baseline ‘normal’ behavior for each IoT device and network segment. Deviations from these baselines trigger alerts and automated responses.
- Automated Orchestration and Response (SOAR): Integrating security tools to automate incident response workflows, such as isolating compromised devices, updating firewall rules, or deploying patches across affected systems.
- Contextual Awareness: Understanding the operational context of IoT devices (e.g., a sensor in a power substation versus a smart meter in a residential area) to prioritize threats and tailor responses appropriately.
ATIR’s Role in Safeguarding U.S. Infrastructure
- Proactive Threat Detection: ATIR’s AI/ML capabilities enable the detection of novel and sophisticated attacks that might bypass traditional security controls, offering a proactive defense posture.
- Scalable Security Management: With millions of IoT devices, manual security management is impractical. ATIR automates monitoring, analysis, and response, making security scalable and efficient across vast infrastructures.
- Reduced Response Times: By automating incident detection and response, ATIR significantly reduces the time from attack identification to mitigation, minimizing potential damage and downtime.
- Improved Situational Awareness: Centralized threat intelligence and analytics provide operators with a comprehensive, real-time view of the security landscape, enabling better decision-making and resource allocation.
- Self-Healing Networks: In advanced implementations, ATIR can enable self-healing capabilities, where systems automatically reconfigure or adapt to neutralize threats without human intervention.
ATIR represents a paradigm shift from reactive to proactive and adaptive security, essential for protecting the complex and distributed nature of IoT-enabled critical infrastructure.
Protocol 4: Secure Over-The-Air (OTA) Updates and Patch Management (SOTAP)
One of the most persistent vulnerabilities in IoT environments is the difficulty of securely and efficiently updating firmware and software on deployed devices. Many IoT devices lack robust update mechanisms, leaving them exposed to known vulnerabilities for extended periods. Secure Over-The-Air (OTA) Updates and Patch Management (SOTAP) is a critical new protocol aimed at standardizing and securing this vital process.
The Essence of SOTAP
SOTAP defines a comprehensive framework for delivering and applying software and firmware updates to IoT devices securely and reliably. Key features include:
- Cryptographic Signing and Verification: All updates must be cryptographically signed by authorized entities, and devices must verify these signatures before applying any changes, preventing the injection of malicious updates.
- Encrypted Update Channels: Update delivery mechanisms are encrypted end-to-end to prevent eavesdropping and tampering during transit.
- Rollback Mechanisms: In case an update introduces unforeseen issues, SOTAP mandates secure rollback capabilities to revert devices to a previous stable state, ensuring operational continuity.
- Delta Updates: To conserve bandwidth and device resources, SOTAP encourages the use of delta updates, which only transmit the changes between software versions, rather than full images.
- Secure Boot and Firmware Integrity: Integration with secure boot processes ensures that only authenticated and verified firmware can run on the device after an update.
- Centralized Management Platforms: SOTAP promotes the use of secure, centralized platforms for managing and deploying updates across large fleets of IoT devices, ensuring consistency and auditability.
How SOTAP Strengthens U.S. Infrastructure
- Rapid Vulnerability Remediation: SOTAP enables the swift deployment of patches for newly discovered vulnerabilities, drastically reducing the window of opportunity for attackers to exploit known weaknesses.
- Maintained Security Posture: Regular and secure updates ensure that IoT devices in critical infrastructure continuously operate with the latest security features and bug fixes, maintaining a strong defensive posture.
- Reduced Operational Risk: By providing reliable rollback mechanisms, SOTAP minimizes the risk of updates causing operational disruptions, which is crucial for always-on infrastructure systems.
- Supply Chain Integrity: Secure update processes extend security assurances beyond the initial deployment, combating threats that may emerge over a device’s long operational life.
- Compliance and Auditability: Centralized, secure update management facilitates compliance with regulatory requirements and provides clear audit trails for all software changes.
SOTAP is indispensable for the long-term security and maintainability of IoT devices within U.S. critical infrastructure, transforming a common weakness into a robust defense mechanism.
The Broader Implications and Challenges of Adopting New IoT Cybersecurity Protocols
The introduction of these four new IoT cybersecurity protocols by 2026 represents a monumental leap forward in protecting U.S. critical infrastructure. However, their successful implementation is not without challenges. These protocols will require significant investment in research and development, standardization efforts across diverse industries, and widespread adoption by manufacturers, integrators, and operators.
Interoperability and Standardization
A key challenge will be ensuring interoperability among devices from different vendors and across various infrastructure sectors. Standard bodies and government agencies will play a crucial role in harmonizing these protocols, preventing fragmentation that could undermine overall security. The National Institute of Standards and Technology (NIST) and similar organizations will be central to defining guidelines and best practices for these new standards.
Resource Constraints and Legacy Systems
Many existing IoT devices, particularly in critical infrastructure, may not have the computational power or memory to support advanced cryptographic algorithms or complex attestation processes. A phased approach to adoption, along with strategies for securing legacy systems through gateways or network segmentation, will be necessary. New deployments, however, should be mandated to incorporate these advanced protocols from the outset.
Talent and Training
The successful deployment and ongoing management of these sophisticated protocols will require a highly skilled cybersecurity workforce. There will be an increased demand for professionals proficient in quantum cryptography, AI/ML for security, and secure embedded systems design. Significant investment in education and training programs will be essential to bridge this talent gap.
Regulatory Frameworks and Compliance
New regulatory frameworks will likely emerge to mandate the adoption of these protocols, especially for critical infrastructure sectors. Compliance will be a significant driver, but it must be balanced with flexibility to accommodate the diverse needs and operational realities of different industries. The goal is to create a robust security baseline without stifling innovation or imposing undue burdens.
Collaboration Between Public and Private Sectors
Protecting national infrastructure is a shared responsibility. Close collaboration between government agencies, private sector companies (including device manufacturers, software developers, and infrastructure operators), and academic researchers will be paramount. Information sharing, joint research initiatives, and public-private partnerships will accelerate the development and deployment of these vital security measures.
Conclusion: A More Resilient Future for U.S. Infrastructure
The year 2026 marks a pivotal moment for IoT cybersecurity protocols in the U.S. critical infrastructure. The introduction of Enhanced Device Identity and Attestation (EDIA), Quantum-Resistant Cryptography for IoT (QRCI), Adaptive Threat Intelligence and Response (ATIR), and Secure Over-The-Air (OTA) Updates and Patch Management (SOTAP) represents a comprehensive and forward-thinking strategy to combat the escalating cyber threats faced by our nation’s most vital systems.
These protocols, individually and collectively, aim to build a more resilient, trustworthy, and secure digital foundation. They move beyond reactive security measures to embrace proactive defense, continuous verification, and future-proof cryptographic standards. While the path to full implementation will present its own set of challenges, the commitment to these advanced security measures underscores a clear understanding of the profound risks at stake.
By embracing these new IoT cybersecurity protocols, the United States is not just responding to current threats but is strategically positioning itself to withstand the cyber challenges of tomorrow. This proactive stance is essential for safeguarding national security, ensuring economic stability, and maintaining the continuous operation of the critical services that underpin modern society. The future of U.S. infrastructure security depends on the successful and widespread adoption of these groundbreaking advancements.
Further Reading:
- NIST Cybersecurity Framework
- CISA Critical Infrastructure Security
- ENISA IoT and Smart Infrastructures (European perspective, relevant for global best practices)