Digital Forensics 2026: US Law Enforcement’s Tech Adaptation
The landscape of crime is continuously evolving, and with the rapid advancement of technology, so too must the methods employed by law enforcement to investigate and prosecute these offenses. By 2026, the realm of digital forensics adaptation in the United States will have undergone a significant transformation, driven by an explosion of data, sophisticated cybercriminal tactics, and the imperative for faster, more accurate investigations. This article delves into how US law enforcement agencies are grappling with these challenges, adapting their strategies, tools, and training to stay ahead in the ever-complex world of digital evidence.
The Exponential Growth of Digital Data: A Forensic Challenge
The sheer volume and velocity of digital data generated daily present one of the most formidable obstacles for modern forensic investigations. Every interaction, transaction, and communication leaves a digital footprint, often scattered across numerous devices, platforms, and geographic locations. Smartphones, smart devices, cloud services, and the ubiquitous Internet of Things (IoT) contribute to an unprecedented data deluge. For US law enforcement, this means that traditional forensic methods, which often involve meticulous manual examination of individual devices, are becoming increasingly inefficient and impractical.
By 2026, the average criminal investigation will likely involve analyzing data from multiple sources: personal computers, mobile phones, social media accounts, encrypted messaging apps, smart home devices, connected vehicles, and even wearable technology. This necessitates a profound digital forensics adaptation, moving towards automated and scalable solutions for data acquisition, processing, and analysis. Agencies are investing heavily in technologies that can ingest vast quantities of data from disparate sources, normalize it, and make it searchable and analyzable in a timely manner. The goal is not just to collect data, but to extract actionable intelligence efficiently, without compromising the integrity of the evidence.
Furthermore, the increasing use of encryption by default on many devices and communication platforms poses a significant hurdle. While encryption is vital for privacy and security, it can impede legitimate law enforcement access to crucial evidence. Agencies are exploring various avenues, including advanced decryption techniques, international cooperation for data requests, and legislative efforts to balance privacy concerns with public safety needs. The debate surrounding ‘backdoors’ and lawful access will undoubtedly continue to shape the legal and technological landscape of digital forensics in the coming years.
Artificial Intelligence and Machine Learning: The New Frontier of Forensic Analysis
One of the most impactful areas of digital forensics adaptation is the integration of Artificial Intelligence (AI) and Machine Learning (ML). These technologies are not just buzzwords; they are becoming indispensable tools for sifting through the mountains of digital evidence. By 2026, AI-powered solutions will be commonplace in US forensic labs, assisting in tasks that were once time-consuming and prone to human error.
Enhanced Data Triage and Prioritization
AI algorithms can rapidly analyze vast datasets to identify patterns, anomalies, and relevant information, significantly speeding up the initial triage process. For instance, AI can be trained to recognize specific types of content (e.g., child exploitation material, drug-related communications, financial fraud indicators) and prioritize them for human review. This allows investigators to focus their limited resources on the most promising leads, rather than spending countless hours manually reviewing irrelevant data. Machine learning models can also learn from past investigations, continually improving their accuracy and efficiency in identifying critical evidence.
Automated Image and Video Analysis
The proliferation of digital cameras and video recording devices means that visual evidence is a staple in many investigations. AI-powered image and video analysis tools can automatically detect faces, objects, license plates, and even specific activities within vast collections of visual data. This capability is invaluable in cases involving surveillance footage, social media content, or images recovered from seized devices. Rather than human analysts painstakingly reviewing hours of footage, AI can highlight pertinent segments for closer examination, drastically reducing investigation timelines.
Natural Language Processing for Textual Evidence
Textual data, from emails and chat logs to documents and web pages, forms a substantial part of digital evidence. Natural Language Processing (NLP), a subfield of AI, enables forensic tools to understand, interpret, and summarize human language. NLP can be used to identify key themes, extract entities (names, locations, organizations), detect sentiment, and even translate foreign language communications, providing investigators with deeper insights into the intent and context of communications. This is particularly useful in complex cases involving multiple suspects and extensive communication records.
Predictive Analytics and Behavioral Profiling
Beyond retrospective analysis, AI also holds promise for predictive analytics in digital forensics. By analyzing historical data and behavioral patterns, AI models could potentially identify individuals at risk of committing certain cybercrimes or predict future attack vectors. While still in its nascent stages and raising significant ethical considerations, this area represents a future direction for proactive law enforcement efforts. The ethical implications and potential for bias in AI algorithms are, however, critical considerations that law enforcement agencies must address as they integrate these powerful tools.
Cloud Forensics: Navigating the Distributed Digital Realm
The shift towards cloud computing has fundamentally altered how data is stored and accessed. Individuals and organizations increasingly rely on cloud-based services for everything from email and document storage to application hosting and infrastructure. This presents unique challenges for digital forensics adaptation, as evidence is no longer confined to a physical device but is distributed across remote servers, often in different jurisdictions.
Jurisdictional Complexities and International Cooperation
One of the primary hurdles in cloud forensics is the jurisdictional maze. Cloud service providers (CSPs) may host data in various countries, each with its own laws and regulations regarding data privacy and access. Obtaining data from a CSP located in another country often requires intricate legal processes, such as Mutual Legal Assistance Treaties (MLATs), which can be time-consuming and cumbersome. US law enforcement agencies are actively engaging in international collaborations and advocating for streamlined legal frameworks to facilitate cross-border data requests.
Data Volatility and Ephemeral Evidence
Data in the cloud can be highly volatile and ephemeral. Users can delete data, or CSPs may have retention policies that automatically purge information after a certain period. This necessitates rapid response capabilities from forensic teams to acquire data before it is lost. Agencies are developing specialized tools and methodologies for acquiring data from various cloud environments, including IaaS (Infrastructure as a Service), PaaS (Platform as a Service), and SaaS (Software as a Service) platforms, each with its own unique architectural and data storage characteristics.
Forensic Readiness of Cloud Service Providers
Law enforcement is increasingly working with CSPs to enhance their ‘forensic readiness.’ This involves encouraging CSPs to implement features that facilitate data preservation and acquisition for legitimate investigations, while still respecting user privacy. This collaboration is crucial for building trust and ensuring that critical evidence is accessible when needed. Standardized protocols and APIs for evidence requests are also being developed to streamline the process.
Internet of Things (IoT) Forensics: A Growing Frontier
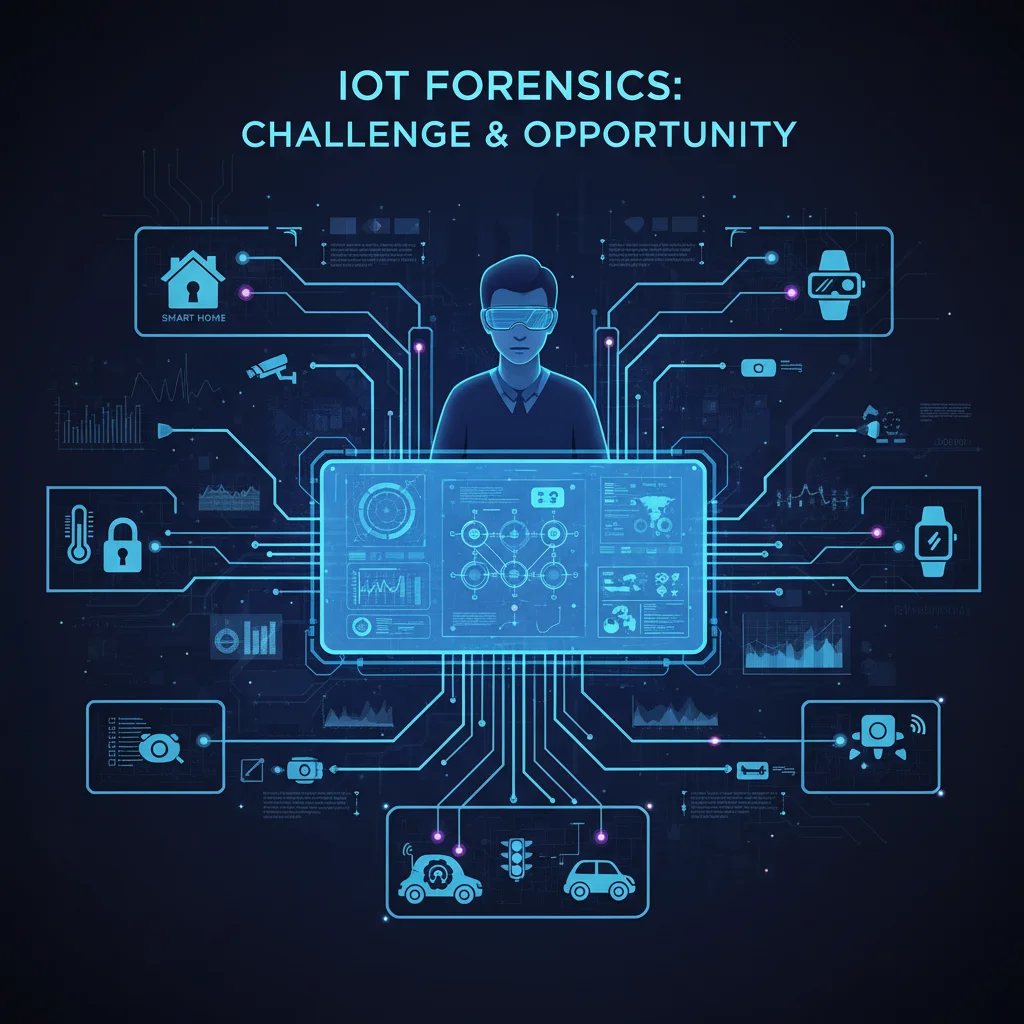
The proliferation of IoT devices, from smart refrigerators and security cameras to connected cars and medical implants, introduces a vast new attack surface and a treasure trove of potential evidence. Each IoT device generates data, often continuously, about its environment, user behavior, and interactions. By 2026, IoT forensics will be a distinct and rapidly evolving specialization within digital forensics adaptation.
Unique Challenges of IoT Devices
IoT devices present unique forensic challenges. They often have limited processing power, storage capacity, and non-standard operating systems, making traditional forensic acquisition techniques difficult or impossible. Many devices rely on cloud connectivity for their functionality, blurring the lines between device-centric and cloud-centric forensics. Furthermore, the sheer diversity of IoT devices, manufacturers, and communication protocols complicates the development of universal forensic tools and methodologies.
Extracting and Analyzing IoT Data
Forensic investigators are developing specialized techniques to extract data from IoT devices, including firmware analysis, memory acquisition, and network traffic interception. The focus is on understanding the data generated by these devices – sensor readings, location data, usage patterns, voice commands – and correlating it with other sources of evidence. For example, data from a smart thermostat could indicate occupancy patterns, while data from a connected car could provide detailed travel histories and even accident reconstruction information.
Security Vulnerabilities as Forensic Opportunities
Ironically, the security vulnerabilities inherent in many IoT devices can sometimes be leveraged for forensic purposes. Exploiting known vulnerabilities might allow investigators to bypass security mechanisms and gain access to internal data. However, this approach raises ethical and legal questions about the limits of law enforcement access and the potential for unintended consequences. The industry is also pushing for ‘security by design’ in IoT devices to mitigate these risks.
Legal and Ethical Considerations in Digital Forensics
As technology advances, so too must the legal and ethical frameworks governing its use in law enforcement. The rapid pace of technological change often outstrips the ability of legal systems to adapt, creating a constant tension between investigative needs and individual rights.
Privacy vs. Security
The fundamental tension between privacy rights and public safety concerns remains at the forefront of discussions surrounding digital forensics adaptation. As law enforcement gains access to more intimate details of individuals’ digital lives, questions about the scope of surveillance, data retention, and due process become increasingly critical. Courts are continually grappling with how to apply Fourth Amendment protections against unreasonable searches and seizures in the digital age, leading to evolving precedents that shape forensic practices.
Data Integrity and Admissibility
Ensuring the integrity and authenticity of digital evidence is paramount for its admissibility in court. Forensic processes must be meticulously documented, and tools must be validated to ensure they do not alter or corrupt evidence. The use of AI and automated tools introduces new challenges in this regard: how do we ensure transparency and explainability in AI’s decision-making process? Can the output of a ‘black box’ AI algorithm be reliably presented as evidence without understanding its internal workings?
Bias in Algorithms
A significant ethical concern with AI in forensics is the potential for algorithmic bias. If AI models are trained on biased datasets, they may perpetuate or even amplify existing societal biases, leading to unfair or discriminatory outcomes. Law enforcement agencies must implement rigorous testing and auditing procedures to identify and mitigate bias in their AI tools, ensuring equitable application of forensic techniques.
Training and Expertise
The complexity of modern digital forensics demands a highly skilled and continuously trained workforce. Law enforcement agencies are investing heavily in recruiting and retaining digital forensic specialists, providing ongoing training in new technologies, tools, and methodologies. Partnerships with academia and the private sector are also crucial for staying abreast of the latest advancements and fostering a pipeline of talent. The demand for digital forensic examiners far outstrips the supply, making talent acquisition and development a critical challenge.
Emerging Technologies and Future Adaptations
Looking beyond 2026, several other emerging technologies will continue to shape the field of digital forensics adaptation.
Quantum Computing’s Impact
While still largely theoretical for practical applications, the advent of quantum computing poses both a threat and a potential opportunity. Quantum computers could theoretically break many current encryption standards, necessitating a shift to quantum-resistant cryptography. Conversely, quantum computing might also offer unprecedented processing power for analyzing complex datasets, potentially revolutionizing forensic analysis.
Blockchain Forensics
The increasing use of blockchain technology, particularly in cryptocurrencies and distributed ledger applications, presents new challenges for traceability and attribution. Forensic investigators are developing specialized techniques to analyze blockchain transactions, identify entities, and trace illicit funds, an area known as blockchain forensics.
Virtual and Augmented Reality Evidence
As virtual reality (VR) and augmented reality (AR) technologies become more mainstream, they will undoubtedly generate new forms of digital evidence. Forensic techniques will need to adapt to acquire and analyze data from these immersive environments, including user interactions, spatial mapping, and biometric data captured within VR/AR systems.
Conclusion: A Continuous State of Evolution
By 2026, digital forensics adaptation within US law enforcement will be characterized by a relentless pursuit of innovation, a strategic embrace of advanced technologies like AI and cloud forensics, and a continuous effort to navigate complex legal and ethical landscapes. The battle against cybercrime is not static; it is a dynamic and ever-evolving challenge that demands constant vigilance and proactive adaptation. Agencies that successfully integrate these technological advancements, foster inter-agency and international cooperation, and prioritize ethical considerations will be best positioned to protect their communities and uphold justice in the digital age. The future of digital forensics is not just about tools; it’s about building a resilient, adaptable, and highly skilled human infrastructure capable of harnessing these tools effectively.
The journey of adaptation is ongoing, and the commitment to continuous learning and development is paramount. As digital technologies continue to permeate every aspect of life, the role of digital forensics will only grow in importance, becoming an indispensable pillar of modern law enforcement.